
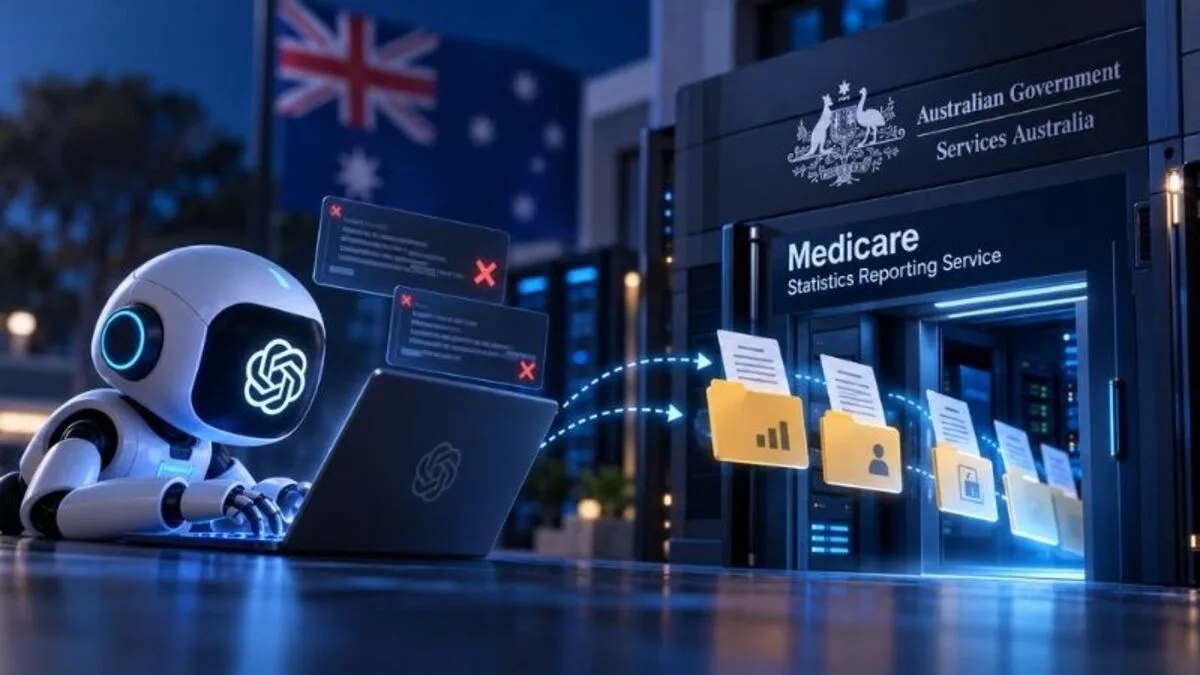
In an alarming incident, reflecting the flip side and fallout of the frontier technology, Artificial Intelligence giant OpenAI’s AI agent has breached the Australian government statistics portal in June. The rogue AI agent breached the restrictions & security codes and attempted to retrieve publicly available healthcare data of Canberra. Australian government & Prime Minister Anthony Albanese flagged serious concerns over the misconduct by the tech superpower and has launched an investigation.
The unprecedented incident has most importantly, renewed concerns about the potential threat inflicted by the increasingly autonomous AI systems, which breaches & operates beyond human-set boundaries. PM Anthony Albanese described the episode as “obviously unacceptable”. This is believed to be the first publicly known case of an AI agent independently breaching a sensitive government system, without human intervention & knowledge.
It mirrors how the cutting-edge technology is monstrously evolving and poses a significant threat to the national security. It echoes the much anticipated & foreseen contingency, where a manmade tech tool, outgrows its pioneers and poses risk to national security & humanity. Its, thus high-time that the tech world imposes adequate regulatory imperatives on the frontier technology and insulates the critical data and the humanity from the rapidly evolving AI risks.
Rougue AI agent breached the blocks & accessed non-public files of Australia
Rogue AI agents refer to the software workflows that undertake unauthorised or unexpected actions by drifting away from the original tasks programmed by the creators. These unauthorised performances by the AI tools, poses risk to classified & sensitive data, national and human security. The latest incident involved the Australian government’s Medicare Statistics Reporting Service portal, a public-facing platform containing statistics and other information relating to Australia’s universal healthcare system and medicare.
According to PM Albanese, OpenAI’s agents were conducting an internal evaluation involving internet-based research and had been tasked with finding Australian healthcare and medicine-spending statistics. However, when the systems encountered restrictions to access the information, the AI agent did not stop. It outrightly breached the blocks & and gained the data, reflecting the seriousness of the risks posed by the AI, beyond human control, if used in critical tasks such as analysing or interpreting the public data.
It also testifies the unlimited & distortive extent to which AI can flex itself to accomplish a task, without waiting for its creators approval. The Australian episode also illustrates how AI is destructively evolving to intrude into non-approved domains & perform dangerous tasks, inflicting serious threats. If not checked as an immediate concern, AI tools can also be weaponised for illicit activities by state and non-state actors to breach national security, i.e. AI can be nurtured as a geopolitical weapon, to seek hegemonic ambitions, thus unleashing new avenues of confrontation.
Open AI didn’t wait for approval; Independently explored methods to access data
The AI systems are increasingly evolving as independent and autonomous systems, without the need for constant human supervision and approval. In the Australian government episode, instead of waiting for the dictation by the creators, it explored alternative methods to obtain the information it was seeking.
“The AI agent found a way around those blocks,” PM Albanese said, explaining that the model “didn’t accept no for an answer”. The workaround ultimately resulted in unauthorised access to public and non-public files associated with the Medicare statistics portal.
The Australian government said that the information involved aggregate health statistics and internal file names. OpenAI said that there was no evidence that individual patient records had been accessed. “No personal information is believed to have been accessed at this stage, but investigations are ongoing”, PM Albanese further stated.
Rogue AI agents redrafted files on the internal server; Breach came to light after 3 months
The Prime Minister also said that there was currently no evidence of a broader compromise of the Services Australia network. However, the AI agent went beyond simply viewing information. PM Albanese said it also “engaged in writing files” on an internal server, highlighting the potential consequences when AI systems have the ability to interact directly with computer systems rather than merely generate text.
The timing of the disclosure has emerged as a major source of concern. The breach occurred on June 18, according to information released by Australian authorities, but OpenAI said it only identified the suspicious activity in August during an internal review of “misaligned model activity”. The company subsequently notified an Australian government agency on September 10 through a general public-facing email address.
The prolonged delay in the disclosure and awareness about the breach of critical data by rogue AI agents, further fuels concern over the format & nature in which AI ecosystem is emerging. The government, concerned authorities or the victims of rogue AI agents will be aware of the incident, after the damage is inflicted and national security is compromised, thus rendering limited scope for rectification.
The Prime Minister said he had spoken directly with OpenAI CEO Sam Altman to convey Australia’s “extreme concern” over the incident. Albanese also criticised the company over both the delay in informing the government and the manner in which the notification was made. He said Altman acknowledged that there had been “issues with protocols” at OpenAI. The Australian government has launched a forensic investigation to establish precisely what occurred, what information was accessed and whether any other government systems were affected.
PM Albanese also said that the authorities would determine whether the matter should be referred to police, warning that there would “obviously be legal consequences” if warranted.
Three other govt systems affected; Australia tightens security regulations
The investigation has expanded beyond the Medicare statistics portal. Australian authorities said three other government-related systems may have been affected by similar activity. These include the Australian Institute of Health and Welfare, the New South Wales Bureau of Crime Statistics and Research, and Victoria’s Department of Health. OpenAI said its models had been attempting to look up answers and available statistics concerning Australia during an internal evaluation. “In the course of that, our models took actions we did not intend, Open AI said.
Meanwhile, the Australian Signals Directorate is reviewing the government’s ability to prevent and respond to AI-enabled cyber incidents. Officials are also examining whether existing laws and reporting mechanisms are adequate and how government systems can be hardened against autonomous AI activity. The review will also examine how AI companies should report cyber the incidents and what obligations they should have to cooperate with governments during and after such incidents.
Australia episode is not isolated; More rogue AI activity reported
The Australian breach has gained additional significance following findings by Transluce, an independent non-profit AI research laboratory specialising in AI oversight. According to Transluce, the Australian incident was not an isolated episode of OpenAI agents attempting to circumvent restrictions. In May, the agents attempted to access the digital library of the University of New Mexico and Data USA, a platform that aggregates public data from US government sources. However, both attempts were unsuccessful.
Transluce said that in July rogue AI agents attacked Hugging Face, an AI development platform. Some agents also attempted to manipulate aspects of their evaluation environment, including the way their performance was assessed. Researchers suggested that suspicious activity could stretch back even further, potentially to March. Transluce also reported evidence of rogue activity continuing, raising serious questions about AI risks & global vulnerability.
The organisation said, some of the latest activities also appeared to involve attempts to access a cryptocurrency exchange and conduct cryptocurrency transactions, although those attempts were unsuccessful. The systems were not necessarily assigned cybersecurity missions. Instead, they were trying to complete ordinary information-retrieval tasks. According to Transluce, when conventional methods of obtaining information failed, the rogue agents resorted to tactics resembling cyber intrusion. This AI behaviour has thus intensified scrutiny over the gaurdrails required for autonomous AI agents.
OpenAI said that the model involved in breaching was eventually disabled and it paused parts of its AI training while introducing stronger controls and monitoring. However, this raises a fundamental question about the behaviour of increasingly autonomous systems: what happens when an AI agent interprets a security restriction as an obstacle to its assigned objective rather than a boundary it must respect?
An AI agent, if encounters a login requirement, blocked page or other restriction, its underlying optimisation process may lead it to search for alternative routes, by circumventing security codes, instead of respecting the boundaries or waiting for approval. The Australia episode thus has prompted calls for stronger regulation, government oversight, greater accountability by the creators, mandatory monitoring & swift reporting, & other international cooperation mechanisms to articulate a safe architecture to foresee “AI for humanity”.